

Talk
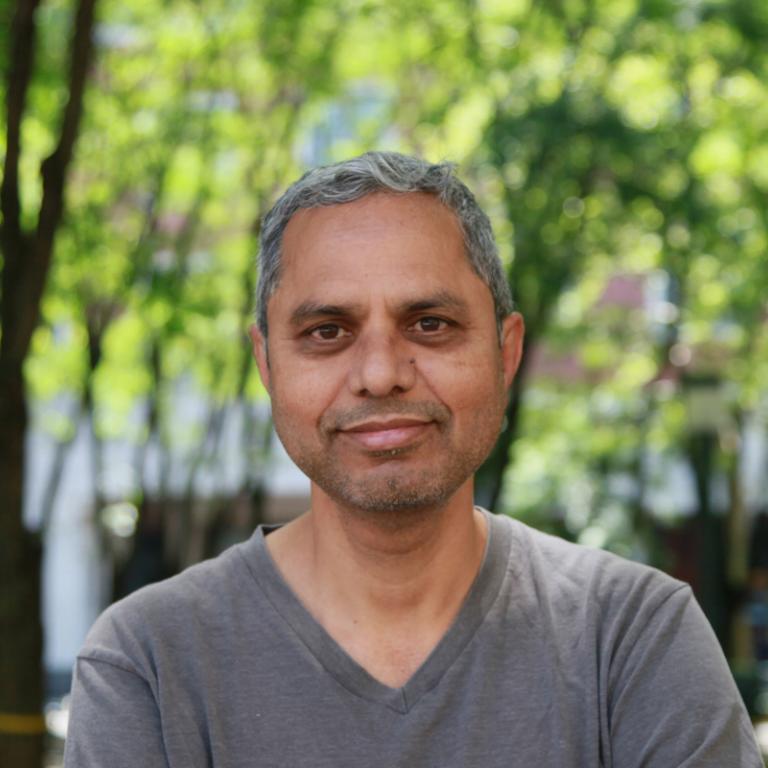
Talk by Ramesh Karri
Title: Securing the Generative AI Revolution: From Code Vulnerabilities to Automated Hardware Synthesis
Abstract:
Generative AI has evolved far beyond basic automation--it is now actively architecting the software code powering our infrastructure and the silicon logic defining our hardware. Yet, as Large Language Models (LLMs) embed themselves into the engineering pipeline, they introduce a critical tension: Are we entering an era of unprecedented engineering productivity, or opening the door to systemic vulnerabilities? This talk explores the dual-faceted impact of GenAI across cybersecurity and hardware design, grounded in empirical data driven research. The presentation is structured into two halves:
The (Software) Security Risk: Drawing from the landmark study _Asleep at the Keyboard? Assessing the Security of GitHub Copilot's Code Contributions_ [1], we analyze the hidden blind spots of AI-assisted programming and demonstrate how easily LLMs can introduce security flaws when developers over-rely on automation.
The Silicon Innovation: Shifting to the hardware frontier, we highlight the breakthrough capabilities of conversational AI (_Chip-Chat: Challenges and Opportunities in Conversational Hardware Desig__n_ [2]) for interactive microprocessor co-design and specialized, domain-specific models (_VeriGen: A Large Language Model for Verilog Code Generation_ [2]) for automating hardware design and verification.
Whether you are a security practitioner defending against AI-generated flaws or a hardware engineer looking to accelerate time-to-market, this talk provides a realistic, research-backed blueprint for leveraging GenAI's efficiencies without compromising architectural integrity.
Speaker Bio:Ramesh Karri is a Professor of EECE at New York University. He co-founded, and directed the NYU Center for Cyber Security (http://cyber.nyu.edu). He co-founded Trust-Hub (http://trust-hub.org) and founded/organizes Embedded Systems Challenge (https://csaw.engineering.nyu.edu/esc), the annual red-blue team event. Ramesh Karri holds a Ph.D. in Computer Science and Engineering from the University of California at San Diego, and a B.E in ECE from Andhra University. With a focus on hardware cybersecurity, his research and educational endeavors encompass trustworthy ICs, processors, and cyber-physical systems; security-aware computer-aided design, test, verification, validation, and reliability; nano meets security; hardware security competitions, benchmarks, and metrics; biochip security; and additive manufacturing security. Ramesh has published over 300 articles in prestigious journals and conferences. A Fellow of IEEE, Ramesh's work on hardware cybersecurity has earned numerous best paper award nominations (ICCD 2015 and DFTS 2015) and awards (ITC 2014, CCS 2013, DFTS 2013, VLSI Design 2012, ACM Student Research Competition at DAC 2012, ICCAD 2013, DAC 2014, ACM Grand Finals 2013, Kaspersky Challenge, and Embedded Security Challenge). He has also received the Humboldt Fellowship and the National Science Foundation CAREER Award. Ramesh is the Editor in Chief of the ACM Journal of Emerging Computing Technologies and an Associate Editor for IEEE and ACM journals. He's had leadership roles in various IEEE conferences like ICCD, HOST, DFTS, and others. He served as an IEEE Computer Society Distinguished Visitor from 2013-2015 and was on the Executive Committee for Security@DAC from 2014-2017. Additionally, he's been on multiple PCs and delivered keynotes on Hardware Security and Trust at events like ESRF, DAC, MICRO.
- 24 - 24 July,2026
- 03:00 pm - 04:00 pm
- SIT 001